
Invicti for DevSecOps
Invicti is a scalable, multi-user web application security solution with built-in workflow and reporting tools ideal for security teams. It’s available as a hosted and self-hosted solution and can be fully integrated in any development or testing environment.

Plus de 5000 grandes organisations font confiance à Invicti


Adaptive Success Conditions
There are a few vulnerability scanners that can be integrated into CI/CD workflows but most of them offer a simple pass or fail conditions. Invicti can be configured further to react to additional circumstances such as vulnerability severity or resource criticality. With such configuration, your CI/CD workflows won’t be hindered by excessively tight conditions and won’t let dangerous vulnerabilities through, either.

Avoid False Positives
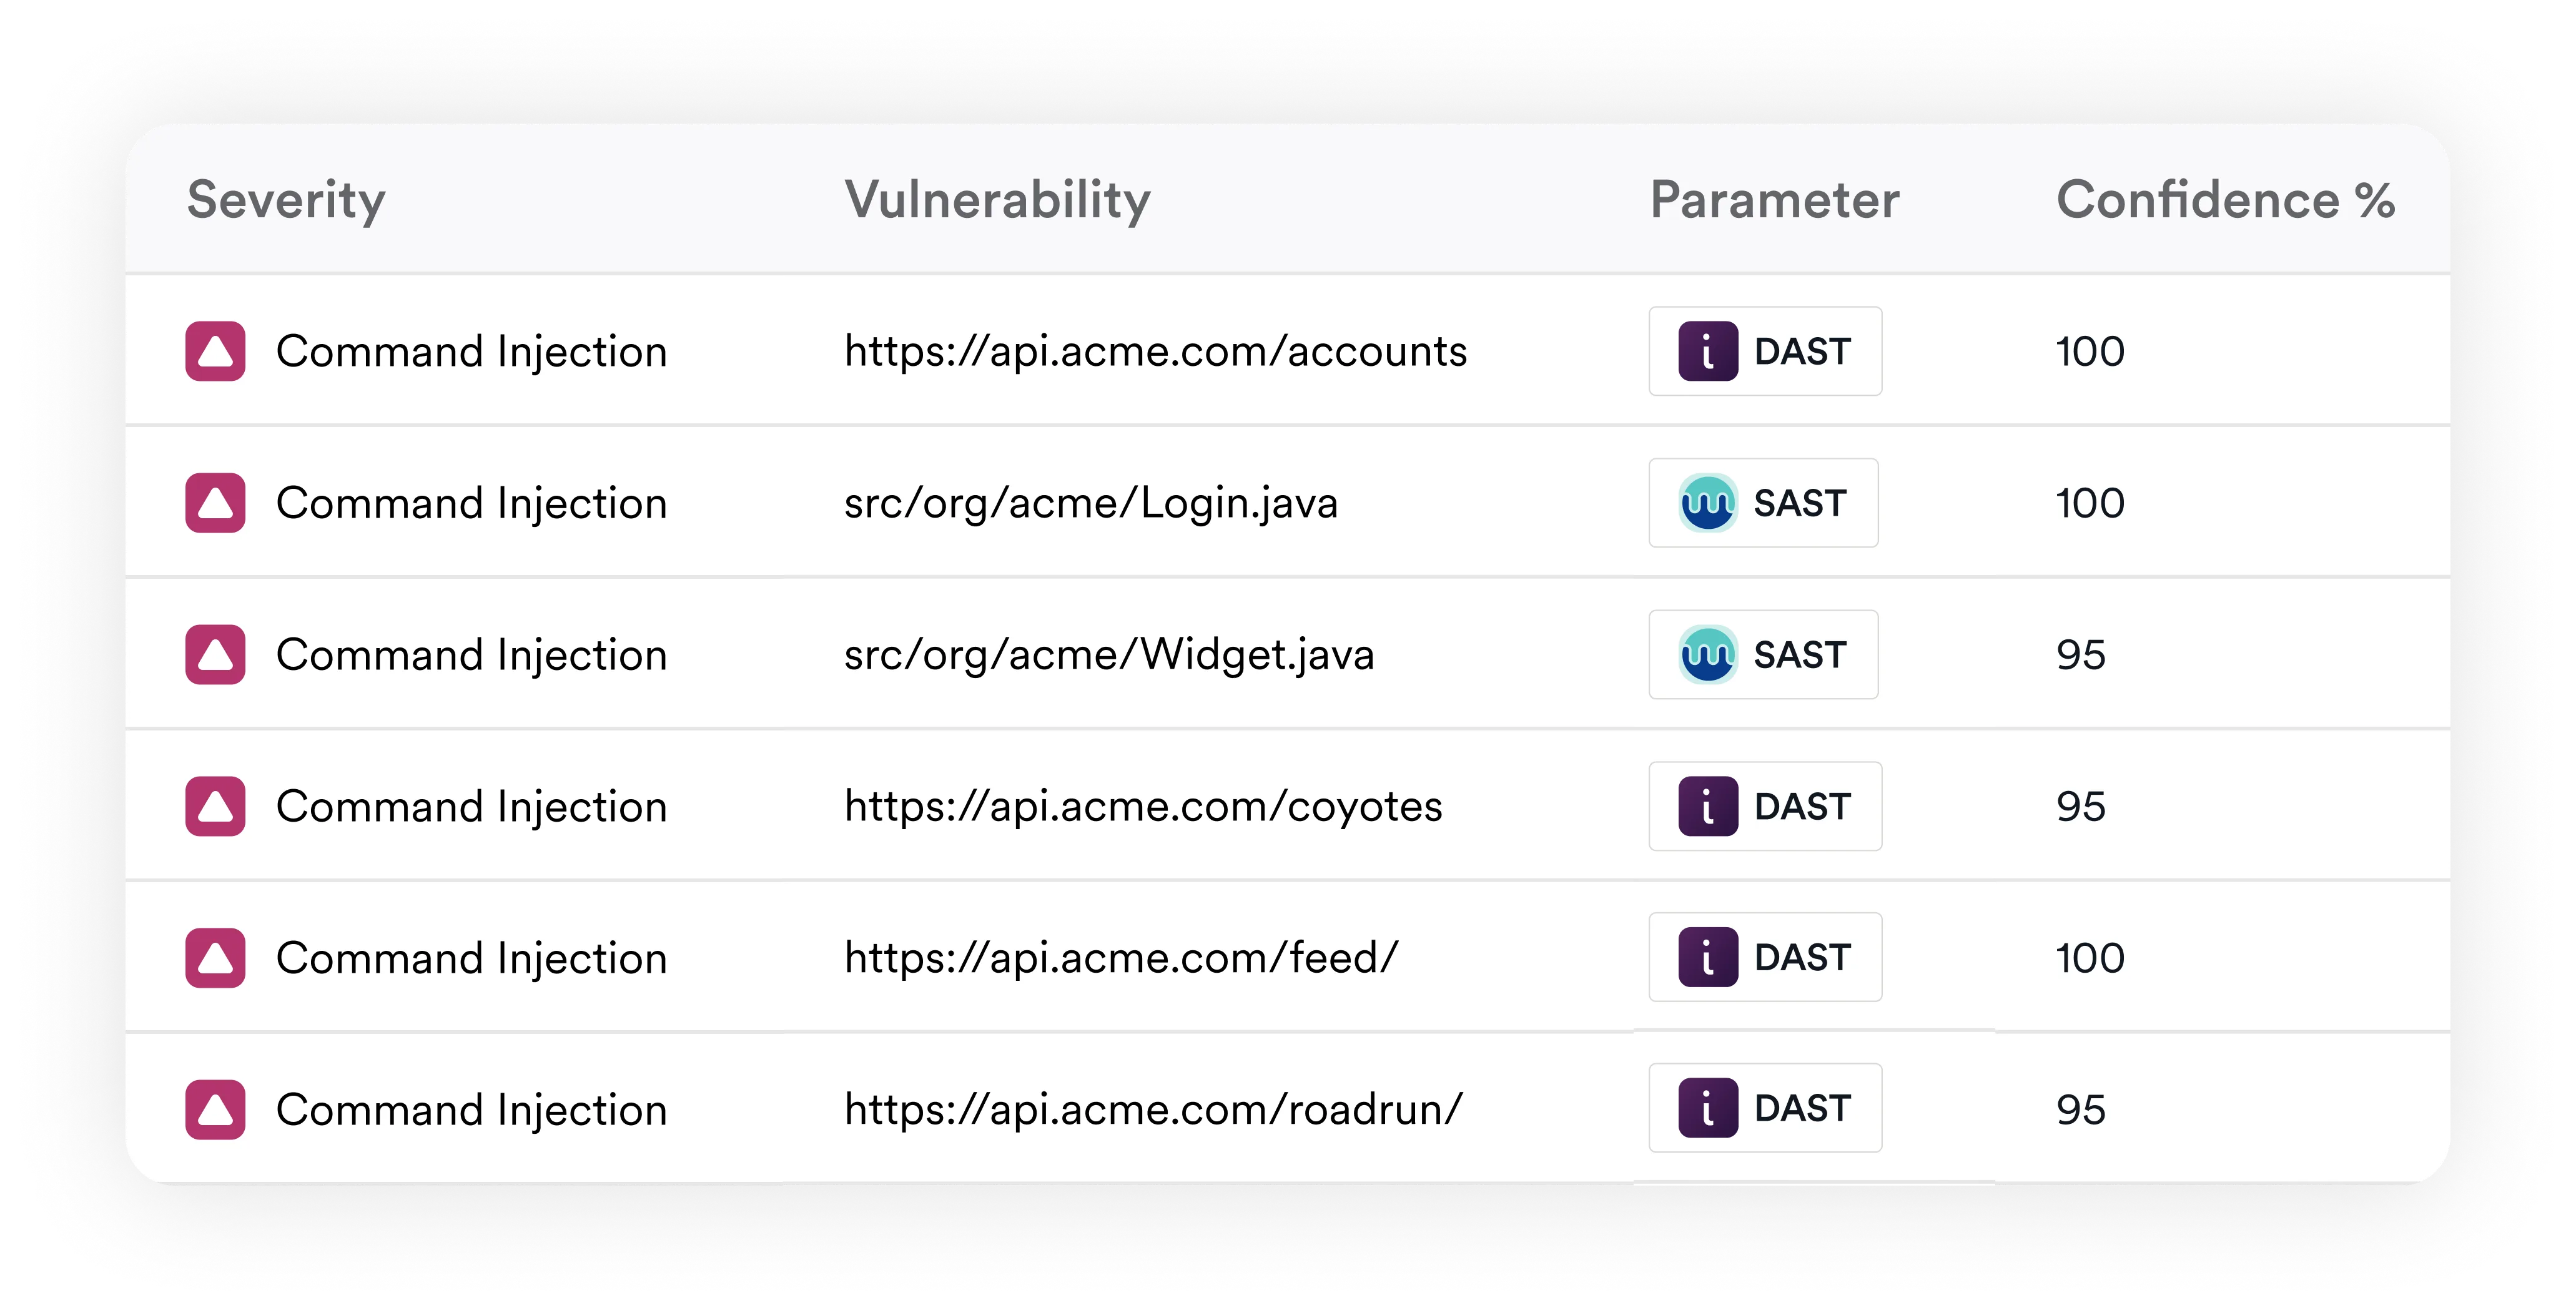
One of the biggest problems that vulnerability scanners face is dealing with false positives. Invicti’s exclusive Proof-Based Scanning system verifies potential vulnerabilities for you, taking tedious manual work off your team’s plate so they can focus on what matters most. If you use Invicti in your CI/CD workflows, you don’t have to worry that builds will keep failing because of problems that do not exist.
Fast and Easy to Integrate
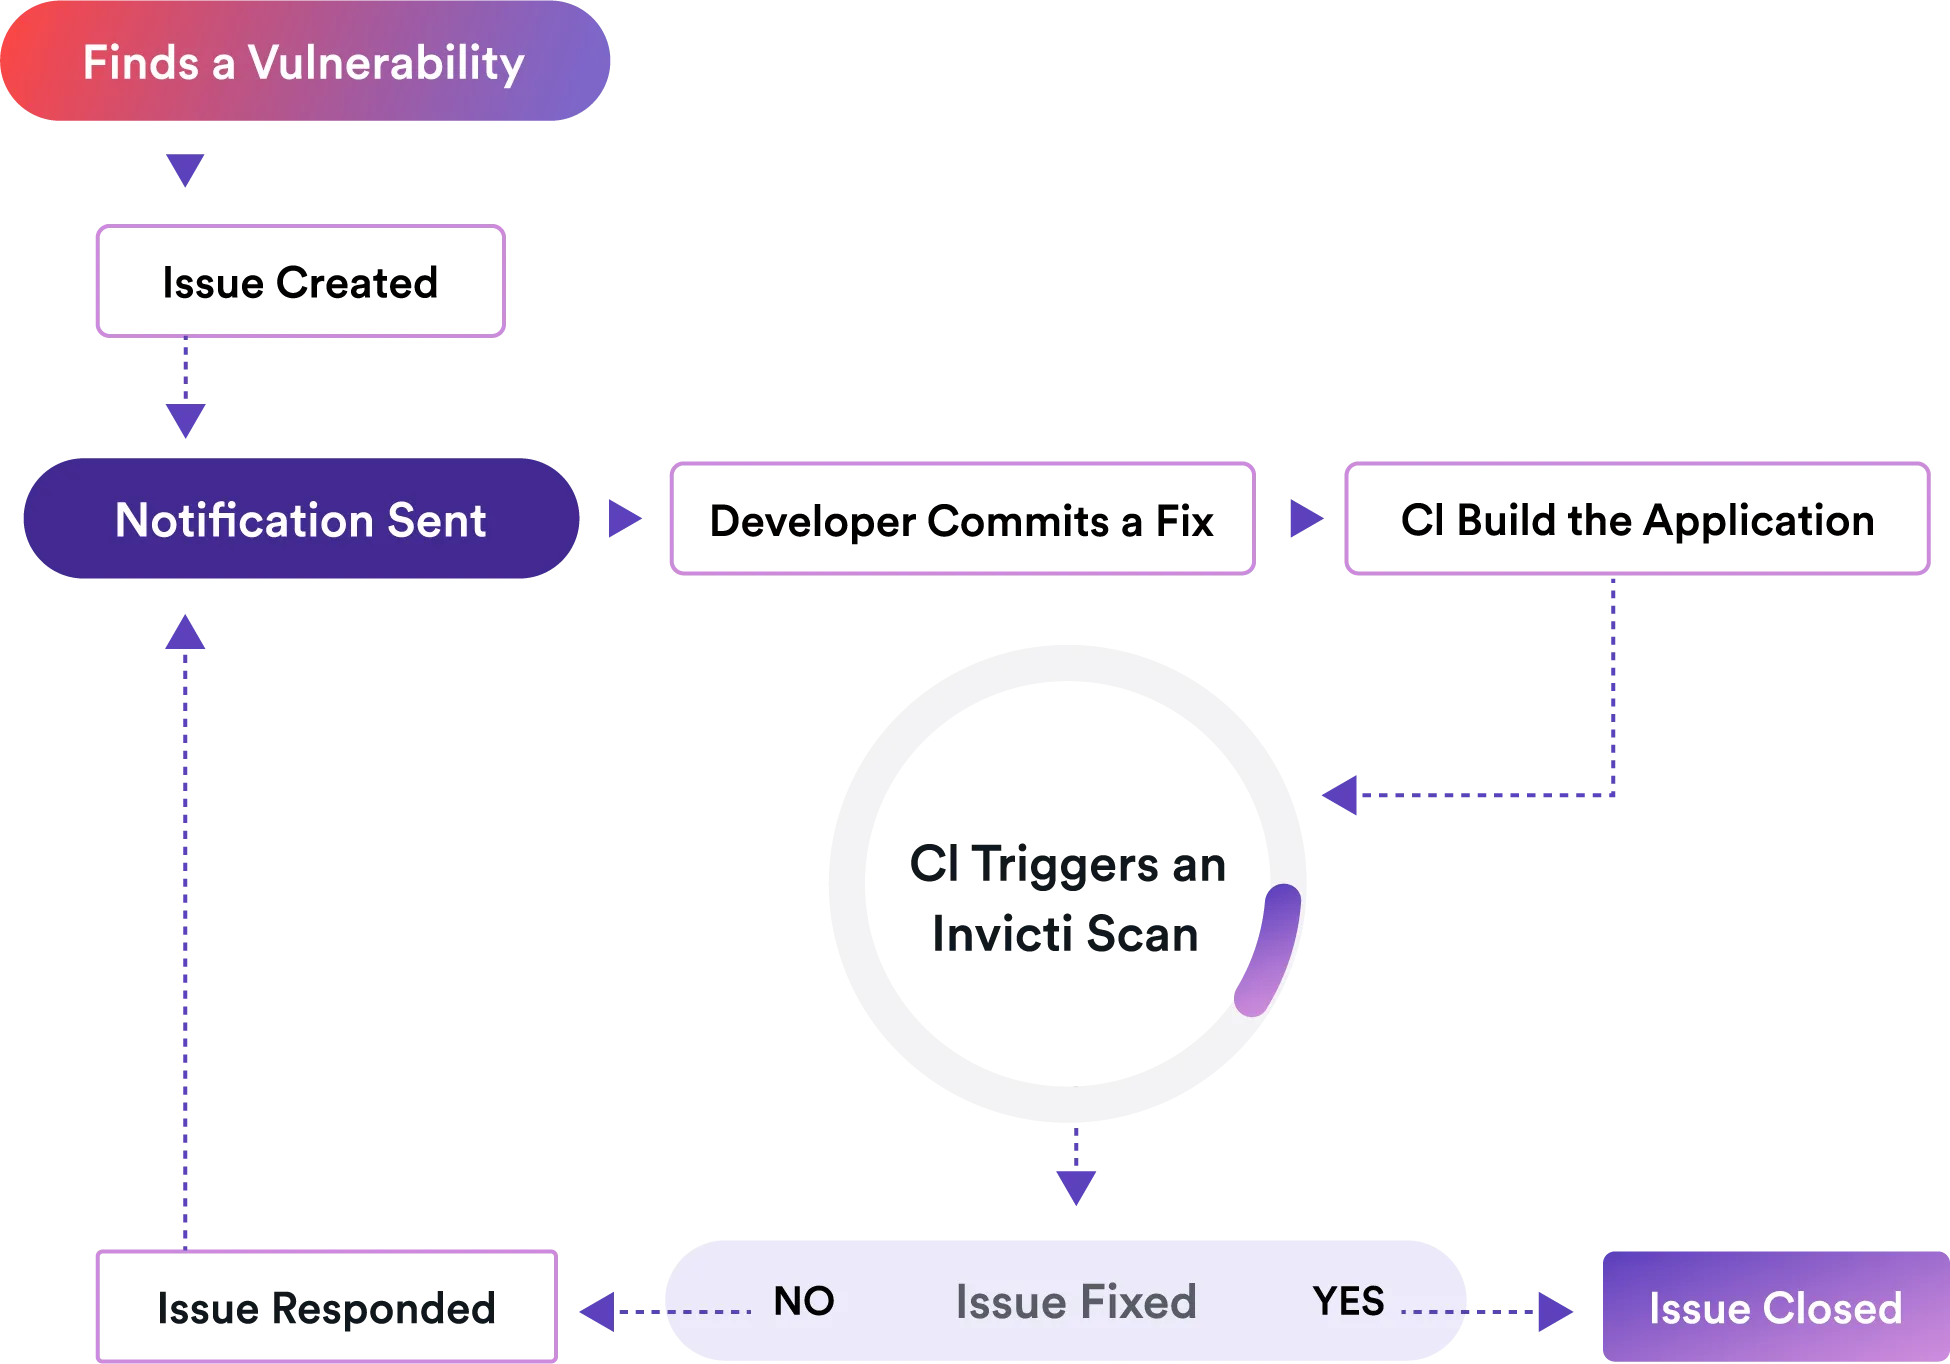
Invicti can perform incremental scans and it works quickly so your builds won’t consume too many resources. The integration process is very easy, so you won’t have to spend a lot of time when configuring CI/CD workflows. Invicti can also be configured to work with several other tools, helping you build a complete automation environment.
Témoignages clients

« Pour la plupart de nos sites web, nous n'avons plus besoin de faire appel à des ressources externes pour les tests de sécurité. Nous pouvons lancer Invicti, effectuer les tests aussi souvent que nous le souhaitons, consulter les résultats et procéder à la remédiation à notre guise. Résultat : le budget que nous consacrions chaque année au test d'intrusion a diminué d'environ 60 % presque immédiatement, pour atteindre l'année suivante environ 20 % de nos dépenses initiales. »

« Invicti a détecté des vulnérabilités web que d'autres solutions avaient manquées. Il est facile à utiliser et à configurer... »

« J'ai eu l'occasion de comparer des rapports d'expertise avec ceux d'Invicti. Invicti était meilleur et a identifié davantage de failles. »

« Invicti est le meilleur scanner de sécurité des applications web en termes de rapport qualité-prix. C'est un logiciel très stable, plus rapide que l'outil que nous utilisions auparavant et relativement exempt de faux positif, ce qui est exactement ce que nous recherchions. »

Save your security team hundreds of hours with Invicti’s web security scanner.
